
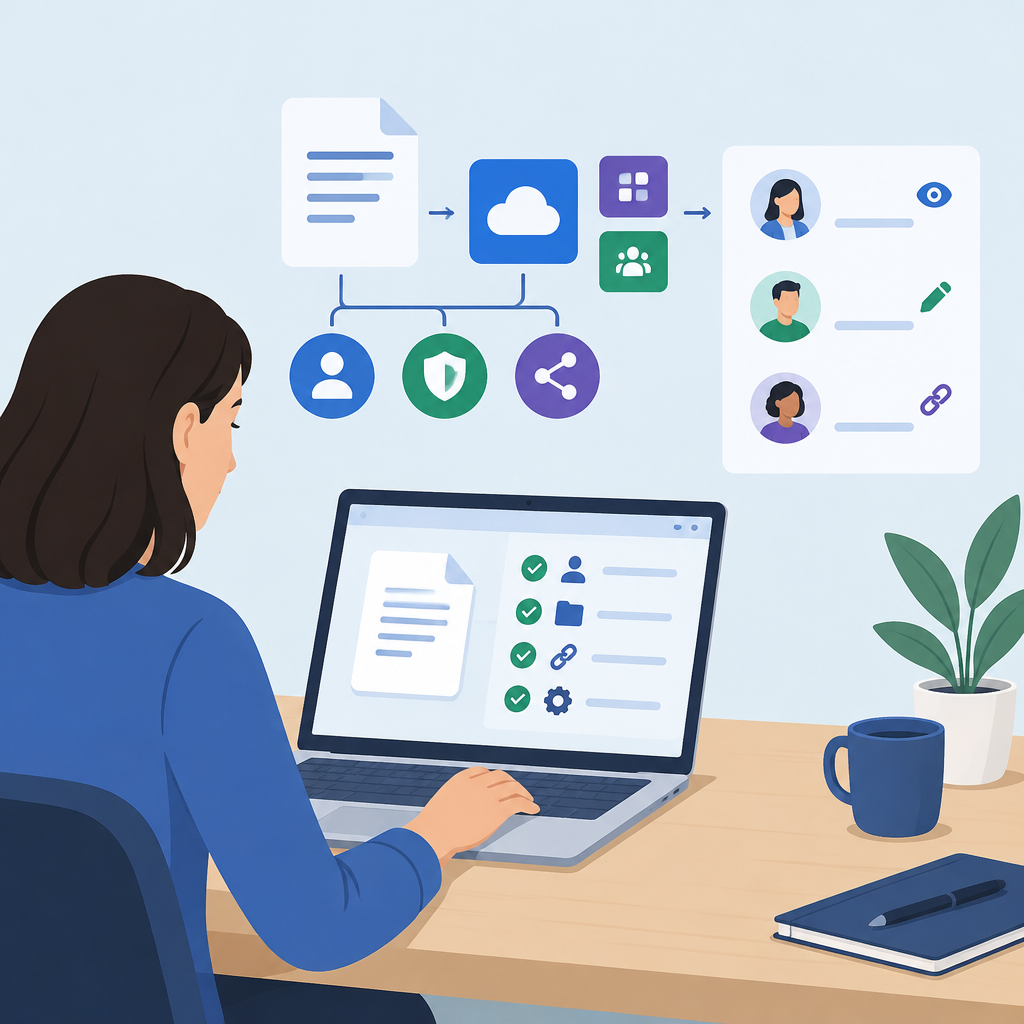
Start with the document, the app, and the reason for sharing
Before you share any document, identify three things: what the file is, which application will handle it, and why the recipient needs access. A document can live in a local editor, a cloud workspace, a team drive, a collaboration app, or a sync client, and each path can expose different permissions. Start by confirming whether the document is in a personal folder, a shared workspace, or an external collaboration space. Then determine the intended audience: one person, a defined group, or anyone with a link. The safest approach is to treat sharing as an access change, not just a file action. If the document contains sensitive business data, regulated data, credentials, or client information, pause and verify that the application itself is authorized to share it in the first place. Also check whether the file type supports the workflow you want. Some formats preserve comments, tracked changes, formulas, or embedded objects, while others strip them or create copies that behave differently. Your stop condition at this stage is simple: if you cannot explain who should get access, what they should do, and where the document is stored, do not share yet.
Check identity, account scope, and whether the app is trusted
Sharing safety begins with the account you are using. Confirm that you are signed into the correct identity, especially if your device supports multiple work or personal accounts. A common mistake is sharing from the wrong tenant, profile, or synced cloud account, which can leak a document into an unintended environment. Review whether the application is managed by your organization, installed on an approved device, and connected through the expected network path. On owned or authorized systems, verify that the app has only the access it needs to store, open, and transmit the file. If the application asks for broad account access, device-wide file access, or permission to scan unrelated folders, consider whether that level of access is necessary for this task. Also check whether the app is handling the document locally, through a browser session, or through a sync agent that may copy the file into another location. If the app is untrusted, outdated, or running under an account you do not recognize, stop and switch to a known-safe path before proceeding. When in doubt, consult vendor documentation or your organization’s policy rather than guessing about permission behavior.
Review file permissions, folder inheritance, and sharing links
Once the application identity is confirmed, inspect the file and folder permissions themselves. A document can inherit access from its parent folder, from a shared workspace, or from a manually assigned link rule, and these layers can create surprises. Look for who can read, edit, comment, reshare, download, print, or export the file. If the application supports roles, compare the role names with their actual powers, because labels such as viewer, commenter, contributor, or editor can mean different things in different products. Check whether the file is protected by an organization boundary, a project group, or a public link that bypasses normal access control. If the document sits in a folder with broader permissions than you intended, the safest fix is often to tighten the parent container rather than adding exceptions one by one. That keeps permissions easier to audit and reduces future mistakes. Before sending the file, verify whether the sharing method creates a live link, a snapshot copy, or an offline attachment. Each option affects revocation, version control, and exposure. If you cannot identify the effective permissions after inheritance is applied, do not distribute the document until you can.
Confirm app permissions for storage, sync, export, and third-party access
Application permissions are not limited to file sharing controls. Many tools can store local caches, sync copies to other devices, export data to integrated services, or grant connected apps access through APIs. Review the permissions that allow the app to read local documents, write temporary files, upload content to cloud storage, or maintain a background sync process. If the document will be sent through a collaboration platform, check whether add-ons, plug-ins, or integrations can see the file contents. A calendar integration, PDF converter, note-taking connector, or automation workflow may receive broader access than you expected. Also inspect whether the app has permission to share outside your domain, publish to a public site, or permit anonymous viewing. These settings matter because a document can remain protected in one place while becoming exposed elsewhere through export or synchronization. If the app offers granular permission review, use it before sharing and again after the share is created. If it does not, rely on the principle of least privilege and disable unnecessary integrations. Stop immediately if the app requests permission that is unrelated to your task, such as access to contacts, microphones, or unrelated folders.
Hypothetical example: shared design brief in a cloud editor
Hypothetical example for practice.
Suppose you are on an owned workstation and need to share a design brief stored in a cloud editor with two reviewers and one editor. First, open the document and confirm that your account is the one that owns or administers the file. Next, check the folder permissions to see whether the document inherits access from a broader project space. If the project folder already allows more people than intended, move the document into a narrower folder or adjust the parent permissions before sharing. Then inspect the app’s sharing panel to confirm whether the link is restricted to named people or open to anyone in the organization. Choose the least permissive option that still allows the reviewers to open the document. If the tool offers role choices, set reviewers to view only and the editor to edit only. Before sending the link, verify whether download, print, or reshare options are enabled, and disable them if the workflow allows it. Afterward, test access from a second authorized account to confirm that the right people can open the file and the wrong people cannot. If any unexpected access appears, revoke the share, correct the setting, and recheck before retrying.
Make reversible changes and verify with a second path
Permission changes should be reversible so you can correct mistakes without recreating the document. Prefer settings that can be undone cleanly, such as revoking a share link, removing a collaborator, or restoring a previous permission state. Before distributing the file widely, keep a note of the original sharing configuration so you can return to it if needed. A practical verification method is to test access from a second authorized account or a separate browser profile that represents the recipient role. This is useful because the sender often sees cached privileges that other users do not. Confirm that the recipient can do only what you intended: open, comment, edit, or download. Also confirm that unauthorized actions fail, such as trying to access the file through an old link or a broader group membership. If the application provides audit logs, review recent events for share creation, permission changes, and access attempts. These logs help you distinguish a real permissions issue from a sync delay or local caching problem. If verification is unclear, stop and wait rather than sending the file further. The safest share is one that can be explained, tested, and rolled back if needed.
Avoid common mistakes with synced devices, caches, and offline copies
Several common mistakes can make a document appear secure when it is not. A frequent error is forgetting that sync clients may copy the file to laptops, phones, or offline folders that have their own local permissions. Another is assuming that deleting a share link removes every copy, when recipients may already have downloaded the document or saved versions elsewhere. Cached previews, offline mode, and mobile storage can all preserve content outside the main application. On managed devices, check whether the app can be opened by other user profiles or whether other services can index the file contents. Also be careful with file forwarding, attached copies, and exported PDFs, because these often bypass the original permission model. If the document includes comments, hidden text, or revision history, confirm whether the recipient should see those elements or only the final version. If not, create a sanitized copy and share that instead of the working file. When troubleshooting, distinguish between access failure and permission denial: one suggests a network, sign-in, or sync problem, while the other suggests the sharing settings are doing their job. Do not keep expanding access just to make a file open; fix the actual issue.
Set clear stop conditions and document the final share
The process ends only when you can state exactly what was shared, with whom, through which application, and under what limits. Record the document name, version or timestamp, sharing method, allowed roles, and any expiration or revocation plan. If the application supports audit history, keep a copy of the relevant event trail or at least note where it can be found. Establish stop conditions before the share goes out: if the wrong account appears, if inheritance cannot be explained, if external access cannot be restricted, or if verification fails, do not proceed. Instead, restore the previous state and investigate. This discipline matters because permission problems often grow after a document is circulated. A clear record makes later troubleshooting faster, especially when different applications, cloud services, and endpoints are involved. It also helps you remove access cleanly when the work is finished. The final check is simple: the right people can reach the document, the wrong people cannot, and you know how to revoke access if the situation changes. If any of those three statements is false, the share is not ready.
Post a Comment