
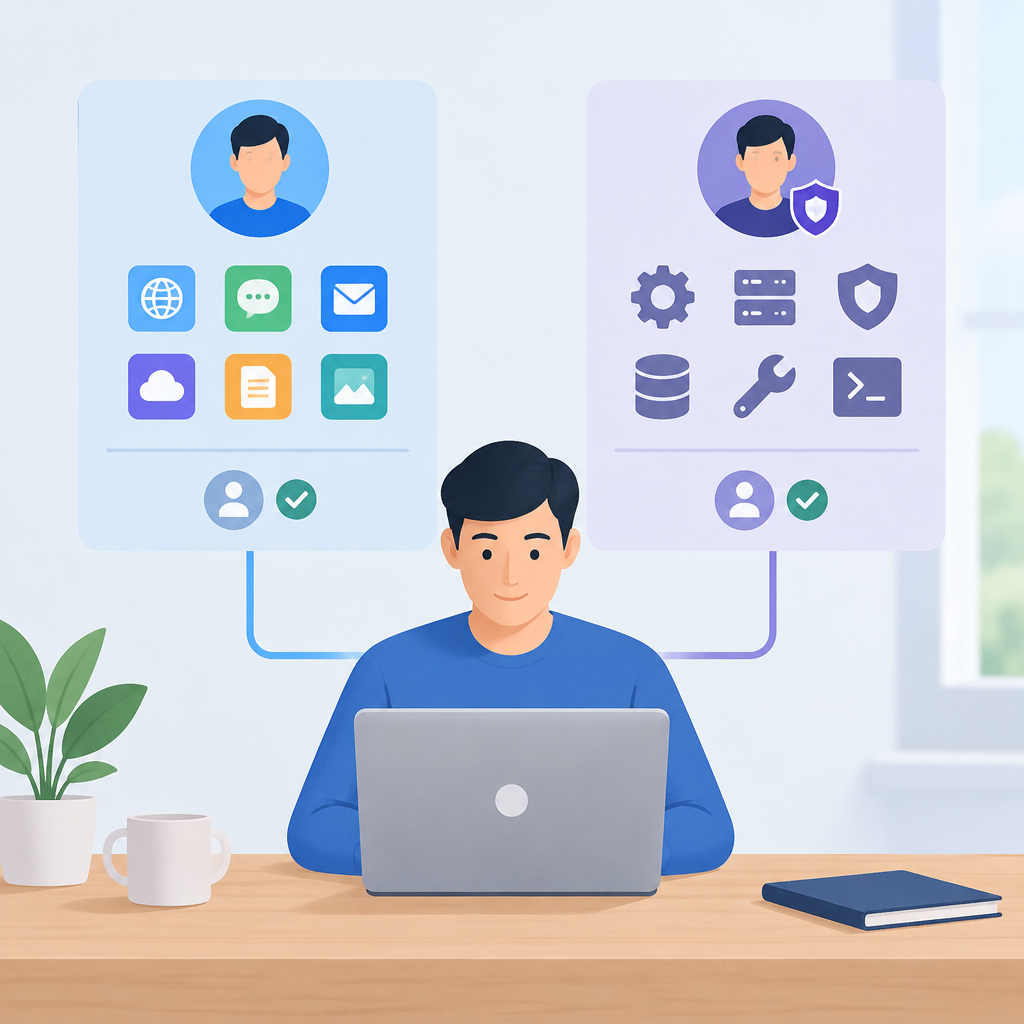
Why account separation matters
Using separate everyday and administrator accounts is one of the simplest ways to reduce accidental damage and limit the reach of malware or human error. A standard account can read email, browse the web, edit documents, and use approved applications without having full control over the device or cloud environment. An administrator account is reserved for installing software, changing security settings, joining systems to a network, creating users, and making configuration changes that affect multiple people or services. This separation does not make a system invulnerable, but it raises the effort needed for a mistake or compromise to spread.
The key concept is least privilege: give each account only the access it needs. That principle applies to endpoints, shared files, identity platforms, cloud consoles, and business applications. If a phishing message tricks a daily-use account, the damage is often smaller when that account cannot silently install drivers, disable protections, or approve risky tenant-wide changes. Before starting, confirm that your device supports a separate admin profile or equivalent elevation model, and make sure you know how to reverse the change if a workflow breaks. If your organization has policies for identity, directory services, or endpoint management, follow those policies and consult vendor documentation for your platform’s exact terms and options.
Plan the split before changing anything
Begin by listing what you actually do each day and what truly requires elevated access. Typical everyday tasks include messaging, browsing, cloud collaboration, document editing, ticketing, and access to approved SaaS tools. Typical administrative tasks include patching software, configuring VPN clients, changing firewall rules, managing user groups, and updating endpoint protection settings. This inventory helps you avoid creating an account structure that is too rigid or too weak. It also reveals hidden dependencies, such as a creative application that stores licensed fonts in a protected folder or a finance tool that needs read-only access to a shared database.
Before creating or changing accounts, collect prerequisites: a recovery method, a second authentication factor if available, a way to reach support if you lock yourself out, and a written list of apps that may request elevation. Decide which accounts will be named clearly enough to avoid confusion. A common pattern is one everyday account for routine work and one separate admin account used only when elevated privileges are necessary. If the platform supports role-based access instead of separate local accounts, use roles to achieve the same separation. Do not remove existing admin access until the new process is tested and you can sign in, elevate, and reverse the change on purpose.
Create or convert the daily-use account
Set up the everyday account first and confirm that it can complete standard tasks without admin rights. On owned or authorized systems, that usually means creating a normal user profile, signing in, syncing email and cloud storage, and checking that file access lands in the expected folders. If you are converting an existing account, remove unnecessary elevated rights only after verifying that the account can still reach required resources. Pay special attention to local folders, shared drives, saved credentials, mapped network locations, and cloud-synced libraries, because these are common points where permissions differ between test and production systems.
A good verification routine is simple: open the applications you use most often, print or export a test file if that is part of your workflow, connect to any required VPN or remote access tool, and confirm that no action prompts for full administration unless it should. If something fails, stop and identify whether the cause is local permissions, group membership, directory policy, or a cloud role assignment. Reversible changes are important here: keep the previous access path documented so you can temporarily restore access while you troubleshoot, then reapply the stricter configuration after the issue is resolved. Avoid granting broad shared credentials just to save time, because that defeats the purpose of the split.
Keep a separate administrator identity and use it only when needed
The administrator account should exist for maintenance, troubleshooting, and controlled changes, not for routine browsing or email. In many environments, this means signing in to the admin account only for tasks that explicitly require elevation, then signing out again. Where systems support privilege elevation, use the admin identity for the minimum time needed rather than staying logged in permanently. This reduces the chance that a malicious download, browser exploit, or mistyped command runs with full control.
A strong practice is to give the admin account a distinct password and a separate multi-factor authentication method if available. Do not reuse the everyday account’s recovery email or app passwords unless your vendor documentation says that is necessary and safe. If your platform supports just-in-time access, temporary role assignment, or approval workflows, use them to limit the window of elevated power. Also remember that the admin account should not be your only recovery option; if it is locked out, expired, or protected by a failed factor, you may need another documented path to regain control. The stop condition is clear: if you find yourself routinely using the admin account for daily work, pause and redesign the workflow instead of normalizing the exception.
Apply the same separation to cloud and online services
Hypothetical example for practice.
The split between daily and privileged access is just as important in cloud consoles, collaboration suites, and hosted business applications. A common mistake is giving one account broad tenant-wide rights because it is convenient. Instead, keep a standard user identity for documents, chat, and routine service use, then assign a separate administrative role only to the account that performs configuration, billing, user management, or security operations. Many cloud systems support roles, groups, and delegated permissions, which can be cleaner than separate accounts if they are implemented carefully.
For example, on an owned or authorized system, a hypothetical small team might keep a standard account for email and file sharing, while a separate role-based admin account is allowed to manage endpoint policies and user onboarding. The team can verify the setup by attempting normal collaboration tasks from the everyday account and by testing a controlled admin change, such as adding a test user to a noncritical group, then rolling it back. If a cloud service offers audit logs, confirm that actions appear under the correct identity and that alerts are delivered to the right mailbox or ticket queue. If role behavior varies by vendor, consult the provider’s documentation rather than assuming that local workstation rules and cloud rules match one another.
Control applications, browsers, and saved secrets
Application behavior often determines whether account separation succeeds or becomes annoying enough to bypass. Browsers, password managers, office suites, remote support tools, development environments, and backup utilities may each store tokens or cached credentials. Review which apps should run under the everyday account and which should be launched only when you need administrative access. Where possible, keep user data, application data, and privileged configuration separate so that a normal session does not inherit admin-only permissions by accident.
Be careful with saved secrets. Browser-saved passwords, synced tokens, and shared clipboard tools can blur the boundary between accounts if they are not scoped correctly. Use a password manager or enterprise secret store that supports distinct identities, and verify that the admin account does not automatically inherit the everyday account’s browsing profile or cloud sync data unless that is an intentional and documented design. If an application asks for elevation unexpectedly, stop and ask whether it truly needs admin access or whether it is simply misconfigured. Common mistakes include launching everything from the admin account “just this once,” installing software directly into a shared profile without checking permissions, and leaving remote sessions open after the task is finished. Those habits make troubleshooting harder and can expose sensitive data to broader access than intended.
Network access, remote administration, and troubleshooting
Hypothetical example for practice.
Account separation interacts with networking because some tasks require access to internal services that are not reachable from a standard public connection. If your environment uses VPN, zero trust access, or remote desktop, confirm which account is allowed to authenticate and whether the network path changes after privilege elevation. Some systems separate human login rights from service access, while others bind access to device compliance or group membership. The principle remains the same: the everyday account should reach ordinary services, and the admin account should be restricted to administrative paths whenever practical.
Hypothetical example on an owned network: a user connects with the everyday account to a collaboration suite over the corporate VPN, then signs in with the admin account only to update a firewall rule or verify a server certificate. If the VPN client refuses the admin session, the right response is not to disable controls, but to check whether the account is in the proper group, whether conditional access is blocking the role, or whether the device lacks a required compliance state. Verification should include testing the connection before any emergency, not during one. If network troubleshooting gets complex, stop after basic checks: confirm identity, route, DNS, time synchronization, and authorization. Do not guess at firewall exceptions or shared credentials, because those often create larger problems than the one you started with.
Maintain, audit, and reverse the change safely
After the split is in place, document it. Record which account is the everyday account, which account is privileged, what each one can do, how the admin account is protected, and how to recover if one is unavailable. Keep the notes concise but specific enough that another authorized person could follow them during a support handoff. Review access periodically because business roles change, devices are replaced, and cloud permissions drift over time. If an account picks up permissions that no longer match the job, remove them promptly rather than waiting for a major cleanup project.
To verify that the separation still works, test two paths: a normal daily task that should succeed without elevation, and an administrative task that should require the privileged identity or an explicit elevation step. If either result is wrong, treat it as a configuration issue. Reversible changes help here: keep a known-good backup of policy settings, export role assignments where appropriate, and know the vendor-supported method for restoring a previous state. Common mistakes include forgetting to update recovery methods, using the admin account for cloud sign-in by default, and assuming one device setting will automatically control all online services. The stop condition is simple: if you cannot explain why a permission exists, remove it after confirming that no documented workflow depends on it.
Post a Comment