
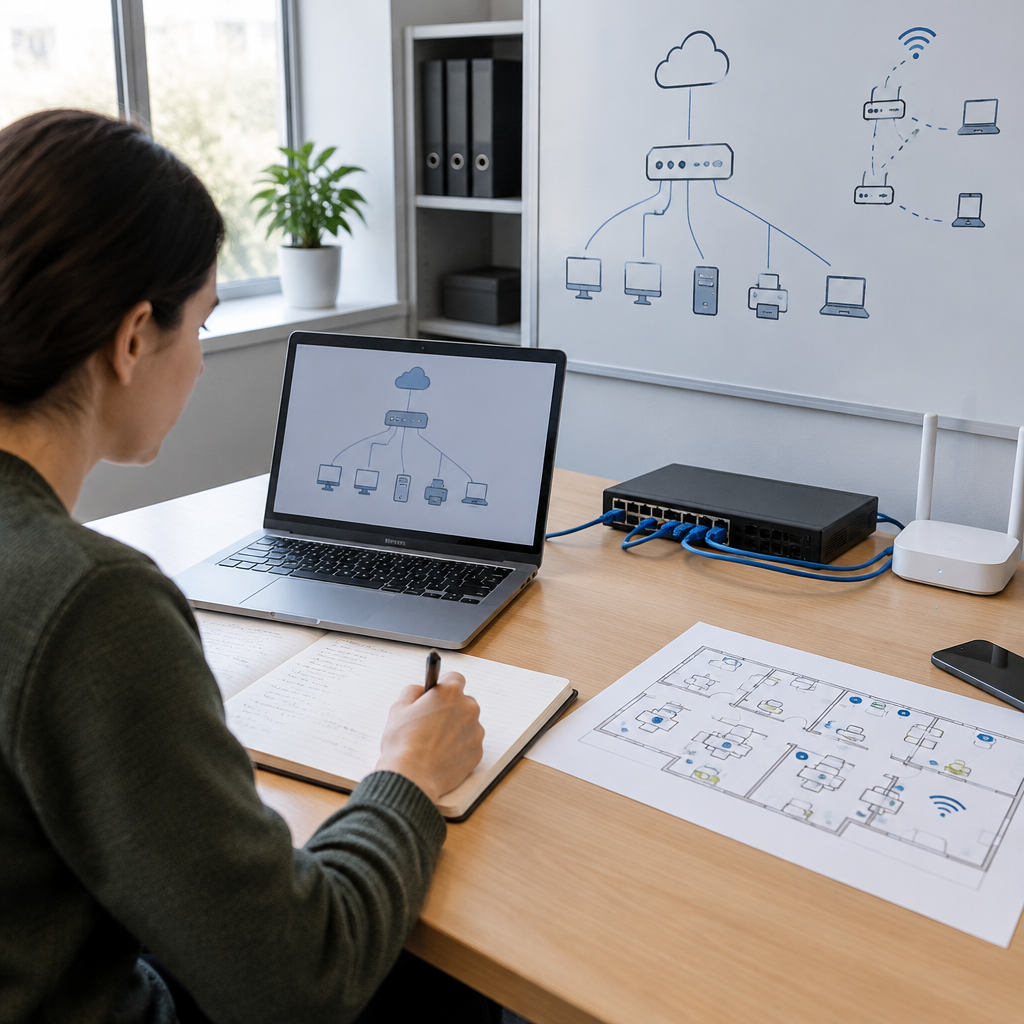
Start With the Purpose and the Boundaries
Before you change anything in a small office network, define exactly why you are mapping it. The goal is not to create perfect architectural art; it is to reduce guesswork, protect shared services, and give yourself a baseline you can compare against after changes. Start by stating the scope in plain language: which room, floor, closet, or branch is included, which devices count as in scope, and which services must keep working during the work. If the change touches internet access, printers, phones, file storage, cloud sign-in, or Wi‑Fi, each of those becomes part of the map.
You also need authority and prerequisites before you begin. Work only on systems you own or are explicitly authorized to manage, and make sure you can reach the router, switch, access point controller, and any cloud admin consoles involved. Collect labels, notebook or spreadsheet templates, and a safe way to export configuration data if the vendor supports it. A good map can be started with a simple table: device name, location, role, connection, IP address, and owner. Keep the map readable enough that another person could use it during troubleshooting, because that is the real test of usefulness.
Inventory the Physical Layer First
The physical layer is often where small office problems begin, so document it before touching settings. Walk the space and identify every networked device: routers, switches, wireless access points, printers, VoIP phones, desktops, cameras, NAS units, conference equipment, and any uplinks to a modem or internet handoff. Note where each device sits, what powers it, and how it connects. If the hardware has visible labels, record them exactly as written. If ports are numbered, note the port numbers and the cable destinations. Where possible, trace a cable from end to end rather than assuming the label is correct.
A useful physical map also records what should not be changed casually. Mark uplinks, trunk links, PoE-powered devices, and any cable that appears to support multiple services. If a switch port feeds an access point, a phone, or another small switch, note that dependency so you do not disconnect an entire branch by mistake. Photograph racks, wall plates, and patch panels for reference, but rely on text notes for the final record. A common mistake is to document only the equipment in the closet and forget the endpoints in offices, shared spaces, or meeting rooms.
Record Logical Addressing and Core Services
Once the physical layout is known, map the logical network. Write down the subnet ranges in use, the default gateway for each segment, DNS servers, DHCP scope details, and any static addresses already assigned to shared devices. In a small office, address conflicts and overlapping DHCP ranges are common sources of trouble, so treat the IP plan as part of the change record. If the network uses multiple VLANs or separated Wi‑Fi networks, list which devices belong in each segment and what traffic is allowed between them. That is especially important when printers, file shares, and management interfaces live on different networks.
Also record the services that make the network useful: local directory services, cloud identity providers, VPN access, print services, backup targets, and remote management tools. If a device depends on a static route, a reserved DHCP lease, or a special DNS name, note it. Verification matters here: confirm address information from the device itself, the router or DHCP server, and any management console rather than trusting memory. For example, if a printer appears reachable by name but not by IP after a later change, your map should help you see whether the issue is DNS, routing, or a duplicate address.
Trace Wireless and Cloud Dependencies
Wireless networks deserve their own section because Wi‑Fi often serves both people and infrastructure. Document each SSID, which access points broadcast it, whether it is intended for staff, guests, or devices, and what network segment it maps to. Note whether the office uses a single shared password, unique credentials, or authenticated onboarding through an identity platform. Also record where access points obtain their management access and whether they are locally managed or controlled through a cloud dashboard. This helps you avoid a change that isolates the APs from the controller or from the internet path they need.
Cloud services can be just as important as local gear. Many small offices rely on hosted email, storage, backups, phone systems, and device management. Write down which apps are business-critical, which devices sync to them, and which local settings influence access. A firewall tweak may look harmless until it blocks time sync, authentication, or software updates used by endpoints. If you use remote collaboration tools or web-based administration, note the sign-in method and recovery path as part of the network map. The practical question is simple: if the office lost internet for an hour, what would still work locally, and what would stop? That answer guides your risk assessment and your rollback plan.
Build a Baseline You Can Test Again Later
A map is only useful if you can verify it. Before making changes, capture a baseline of how the network behaves now. Test a sample of important paths: internet access, local name resolution, printing, file access, VoIP registration, VPN sign-in, and wireless roaming if relevant. Use the same devices you expect to depend on after the change. Write down the result in plain language, including whether the connection is stable, slow, intermittent, or unavailable. If your tools allow it, save copies of configuration exports, screenshots, and simple command outputs for addresses, routes, and DNS results. Keep these records with the map so you can compare before and after without relying on memory.
This baseline should also include a check of security-related settings that affect availability. Confirm which accounts have admin access, whether multifactor authentication is enabled where required, and whether remote management is restricted to trusted sources. If backups exist, verify that they are recent enough to restore configuration, not just data. The point is not to test everything forever; it is to establish enough evidence that later changes can be judged fairly. A common error is to measure only whether the internet works and ignore internal dependencies, which leads to false confidence when a printer, guest network, or cloud-linked service fails afterward.
Use a Simple Dependency Map to Reveal Hidden Coupling
Hypothetical example for practice, not a real case.
Small offices often have hidden dependencies that are easy to miss until something breaks. Draw a simple dependency map showing which device or service depends on which other one. For example, a workstation may need the switch, DNS, file share, authentication service, and cloud license check to all succeed before the user can work normally. A network printer may depend on a static IP, a reserved DHCP lease, and a print server queue. A wireless access point may depend on the switch port for power, the management VLAN for control, and the internet link for cloud monitoring. This type of mapping is more useful than a pure topology sketch because it shows failure chains.
For a hypothetical authorized example, imagine a 12-person office with one modem, one firewall, two switches, three access points, one NAS, one VoIP provider, and a cloud-based identity platform. If the firewall is replaced, the map should show whether the NAS backup job uses a local destination, whether the phones register directly to the provider, and whether the access points need their controller reachable during reboot. That makes it easier to choose a maintenance window and a fallback option. The main mistake to avoid is assuming that a device has only one role; many small office devices are carrying more services than their labels suggest.
Plan Reversible Changes and Safe Execution
Once the map is complete, turn it into a change plan that can be reversed. Write down exactly what will be modified, what the expected result is, how to verify success, and how to restore the previous state if the change misbehaves. Reversible changes are safer when you can make one adjustment at a time instead of bundling several unrelated actions together. For instance, if you are renumbering a subnet, moving a printer, and replacing a wireless SSID, separate those tasks or at least stage them in a controlled order. Keep backups of configuration files and record the time of each change so you can correlate it with any user reports.
Your execution plan should also include a pause point. Stop after each major step to verify connectivity from a known-good test device. If the network segment goes dark or latency spikes unexpectedly, do not press on hoping it will settle down. Re-check the map, confirm the correct switch port or VLAN assignment, and compare the live state against the baseline. In small offices, the fastest way to create a long outage is to make multiple undocumented changes while assuming that a later reboot will fix everything. A careful plan is slower at the start but much easier to unwind if something goes wrong.
Know the Stop Conditions and Keep the Map Current
A good mapping process ends with clear stop conditions. Stop immediately if you lose management access to core gear, if an unknown device appears to be taking over an address, if the wrong subnet becomes active, or if a security control begins blocking legitimate administration. Stop if you cannot explain why a service changed, because continuing without understanding the cause usually makes recovery harder. When a stop condition is reached, restore the last known-good configuration, validate the baseline again, and update the map with what was discovered. That is not a failure; it is disciplined troubleshooting.
After the work is complete, treat the map as a living document. Update it whenever a switch port changes purpose, a new access point is added, a printer moves rooms, or a cloud service begins depending on a different account or DNS name. Store the map where authorized staff can find it, but avoid exposing sensitive credentials inside it. A practical office map is concise, dated, and easy to check during an incident. If you can hand it to another administrator and they can identify the critical devices, dependencies, and rollback path, the map has done its job.
Post a Comment